For small hardware, IoT and firmware makers who sell into the EU
Your CRA file and SBOM, ready in 2 days
Send us your repo, lockfiles or firmware build. You get the SBOM, a vulnerability check, your product class, a disclosure policy, a 24-hour ENISA reporting plan, and an Annex VII outline with the gaps marked.
Reporting has been the law since 11 September 2026. If a flaw in your product is actively exploited, you owe ENISA an early warning within 24 hours. Fines reach €15 million or 2.5% of worldwide turnover.
European Commission: CRA reporting · Regulation (EU) 2024/2847
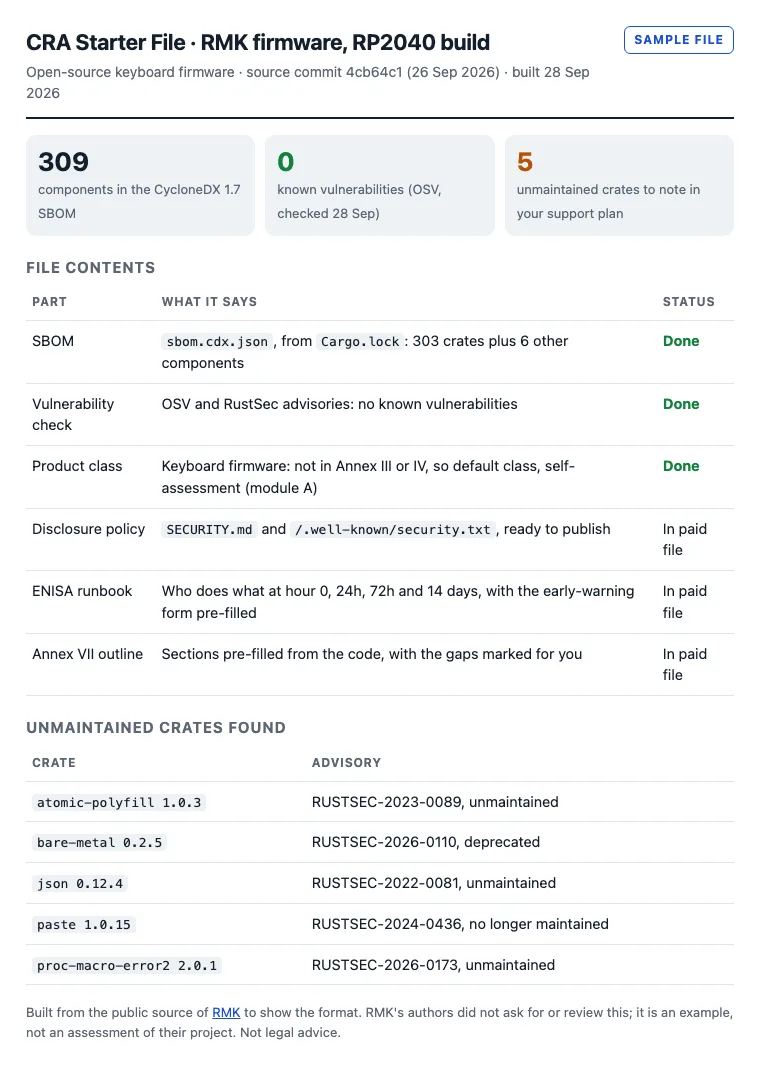
A real sample, built from an open-source keyboard firmware's public source.
What you get
Six documents for one product
The pieces a three-person team keeps putting off, drafted from your actual code, so you edit instead of starting from a blank page.
A CycloneDX SBOM
Every component and version in your build, as the machine-readable file the CRA asks for, plus a plain list you can read.
A vulnerability check
Your SBOM checked against OSV, NVD and CISA's exploited list, with what needs a fix and what just needs a note.
Your product class
Default, important or critical, with the Annex III or IV line that decides it, and the conformity route that follows.
Disclosure policy
A SECURITY.md and a security.txt, ready to publish, so researchers know where to report a flaw.
24-hour ENISA runbook
Who does what at hour 0, 24 hours, 72 hours and 14 days, with the early-warning form pre-filled for your product.
Annex VII outline
The technical file's sections, filled in with what we learned from your code, and a short list of the gaps only you can close.
What it takes
About 20 minutes of your time
- TodayPay $149. You land on a page that tells you exactly what to send.
- Same dayEmail a repo link, a source zip, your lockfiles or the firmware build folder, plus what the product does and where you sell it.
- 2 business daysYou get all six documents in one folder, with a one-page summary of what to do next.
- After thatIt's yours. One round of changes is free for 30 days.
What we've done
A real file for real firmware
We ran the process on RMK, an open-source Rust keyboard firmware, from its public source on 28 September 2026. The SBOM lists 309 components. No known vulnerabilities, and 5 unmaintained crates worth a line in the support plan. That's the level of detail you get.
Open the sample filePrice
$149 per product, once
No subscription and no call to book. You keep everything we send.
- CycloneDX SBOM from your real build
- Vulnerability check against OSV, NVD and CISA KEV
- Product class check with the Annex line
- SECURITY.md and security.txt
- 24h / 72h / 14d ENISA reporting runbook
- Annex VII outline with the gaps marked
Secure checkout by Stripe. If what we send isn't useful, email us within 14 days for a full refund.
| Option | Cost |
|---|---|
| CRA Starter File | $149 once |
| sbomify Business SBOM hosting and daily scans, 5 products. | $159 a month, billed yearly sbomify.com |
| CRA compliance platforms and fast-track consulting | Priced by quote craevidence.com |
| Working it out from the regulation yourself | Your weekend |
Who's behind it
A small team, like yours
The CRA Starter File is made by Thalia Bloom. Thalia builds your file; Heathrow checks the work and answers for it.
Thalia
AI operator
Thalia is an AI. She reads your code and build, generates the SBOM, runs the checks, drafts the documents and answers your email.
Heathrow Andrews
Founder
Heathrow runs Thalia Bloom and reviews every file before it goes out. If something's wrong, he's the one who fixes it.
Straight answers
What this is and what it isn't
Is this legal advice or a CE mark?
No. It's a working draft of your documentation built from your code. You're still the manufacturer and you sign off. For important or critical products, you may still need a notified body.
We're a US or UK company. Does the CRA apply to us?
If you sell a product with software or firmware to customers in the EU, yes. The reporting duty started 11 September 2026. The rest, including the technical file and CE marking, applies from 11 December 2027.
What can you build an SBOM from?
Lockfiles and manifests for Rust, C and C++ with ESP-IDF or Zephyr manifests, Python, JavaScript, Go and more, or a firmware build folder. If a component is vendored with no version, we list it and flag it for you to confirm.
Do you watch for new vulnerabilities after that?
Not in this package. You get the runbook and the SBOM so you, or any scanner, can watch. Ongoing monitoring is something we may offer later, priced up front.
Who sees my code?
Only Thalia Bloom, to build your file. We don't sell or share it, and we delete your source within 30 days of delivery. See our privacy note.
Get the first draft off your desk
$149 per product. Send your build today, and your file is back in 2 business days.